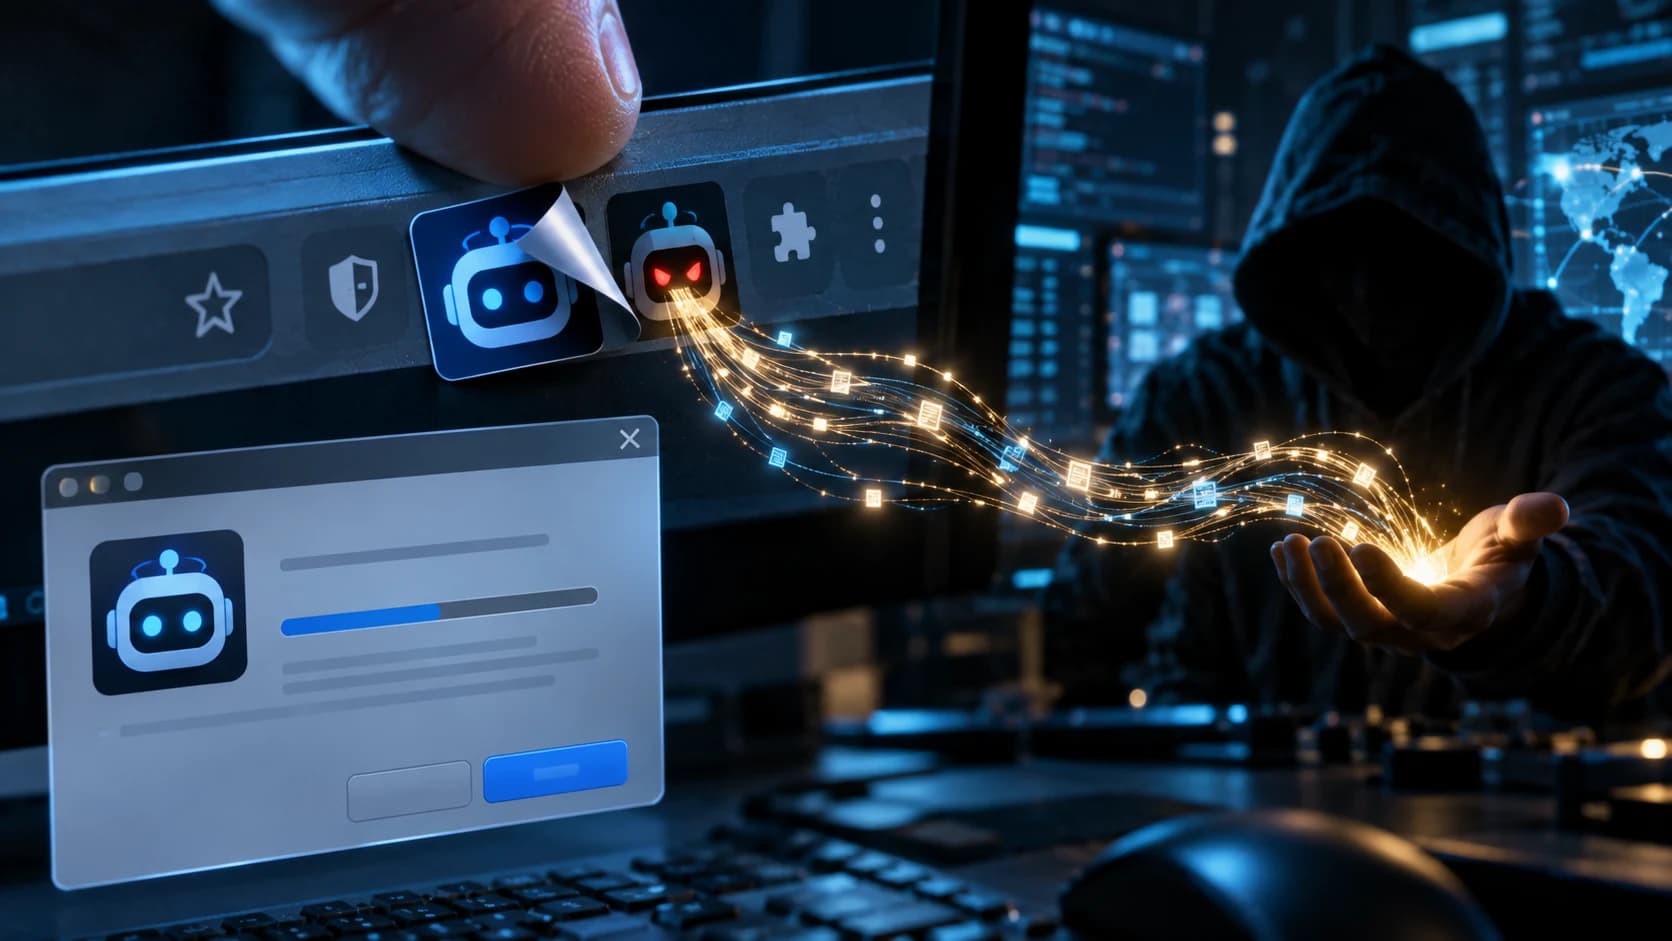
A fake AI crypto-trading tool is being used to install malware that quietly replaces browser wallet extensions with credential-stealing copies, according to HP's threat research team, in findings reported by CryptoSlate on September 18, 2026. The malware, named Needle Stealer, targets seven browser-based wallets and swaps the legitimate extensions for lookalikes built to harvest login details and seed data.
The lure is the part worth paying attention to. Instead of a crude phishing email, the campaign wraps itself in the language every trader is hearing right now: an AI tool that promises to automate crypto trades. That framing lowers the guard of exactly the people who hold assets worth stealing.
The swap that makes this dangerous
Most wallet-draining malware works by phishing a seed phrase or tricking a user into signing a malicious transaction. Needle Stealer takes a more patient route. It replaces the real extension in the browser with a copy that looks and behaves like the original, so the victim keeps using what they believe is their normal wallet while credentials flow to the attacker.
That design matters because it removes the moment of suspicion. There is no unfamiliar popup, no obviously sketchy signing request. The extension icon sits where it always sat. The user logs in as usual. The theft happens underneath a familiar interface, which is why this class of attack tends to go unnoticed until funds are already gone.
HP's report notes the campaign used signed Microsoft software to help the payload move without tripping standard defenses, per CryptoSlate. Code signing is meant to be a trust signal. When attackers get their hands on that trust, security tools that key off signature status have less to catch.
Browser wallets sit in the blast radius
The seven targeted wallets are all browser extensions, and that is not a coincidence. Extension-based wallets keep keys inside the browser environment, which is convenient for daily use and connecting to apps, but it also means anything that can modify the browser can potentially reach the wallet. A swapped extension is a direct line to whatever that wallet touches.
This is the recurring trade-off with hot wallets that live next to your everyday browsing. Convenience and attack surface grow together. A self-custody wallet puts you in control of your keys, but control also means the security burden sits with you, not a custodian who can freeze a compromised account.
For anyone who spends directly from a browser-connected wallet, including holders of cards that draw from non-custodial balances, the exposure is not abstract. If the extension feeding your card is compromised, both your holdings and your spending rail run through the same poisoned software.
Practical steps if you use an AI trading tool
The direct defense here is boring and effective. Do not install trading automation, browser tools, or "AI assistants" from links in social posts, direct messages, or search ads. Get software from the vendor's verified site or the official extension store, and check the publisher.
If you already installed an unfamiliar AI trading tool recently, treat any browser wallet on that machine as potentially compromised. Move funds from a clean device, revoke token approvals, and reinstall wallet extensions only from official sources after confirming the machine is clean. A hardware wallet keeps the signing key off the browser entirely, which blunts an extension swap because the private key never lives where the malware can copy it.
For active balances, splitting funds helps. A small hot balance for daily spending and the bulk held in cold storage limits what a single compromised extension can reach. Regular review of connected apps and token allowances closes another common path attackers use after the initial breach.
The wider pattern is the more useful takeaway. As AI tools flood the market, "AI-powered" has become a trust word attackers borrow. The same instinct that makes traders eager to try a new automation edge is the instinct this campaign is built to exploit. Slowing down long enough to verify where a tool actually comes from is now part of custody hygiene, not an optional extra.
Overview
HP's threat researchers, as reported by CryptoSlate on September 18, 2026, found a fake AI crypto-trading tool distributing Needle Stealer, malware that replaces seven browser wallet extensions with credential-stealing copies and leans on signed Microsoft software to avoid detection. The attack hides behind a familiar interface, which makes it harder to spot than typical phishing. Users should install tools only from verified sources, keep signing keys off the browser where possible, and treat any machine that ran an unknown AI trading app as compromised until proven clean.